Application Security
We check web applications for the most common vulnerabilities (unauthorized data access, injections, insecure sessions, outdated dependencies) and fix them. For new apps, we build security in from day one instead of patching it on later.
Who it's for
- Apps that handle personal, medical or financial data
- Companies that must demonstrate GDPR compliance
- Products ahead of a big launch or a client's audit
- Old apps that haven't been updated in a long time
What you get
- 01A security audit based on the OWASP Top 10
- 02A report of vulnerabilities found, ranked by risk
- 03Fixes for the issues found
- 04Updates of outdated, vulnerable dependencies
- 05GDPR recommendations: what data you keep, for how long and who can access it
Relevant work
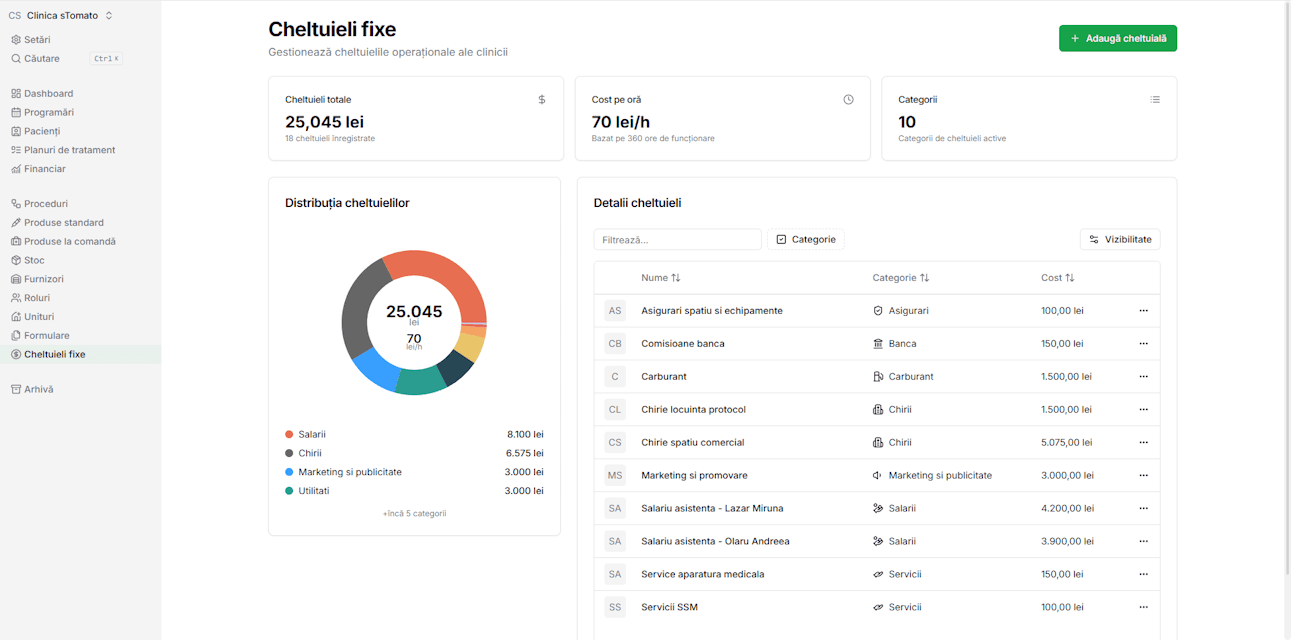
sTomato - Dental Clinic BI Platform
Complete B2B SaaS app for dental clinic management and business intelligence, helps dental clinics reduce costs and increase profitability through real-time financial insights and automation.
Next.js / TypeScript / Prisma
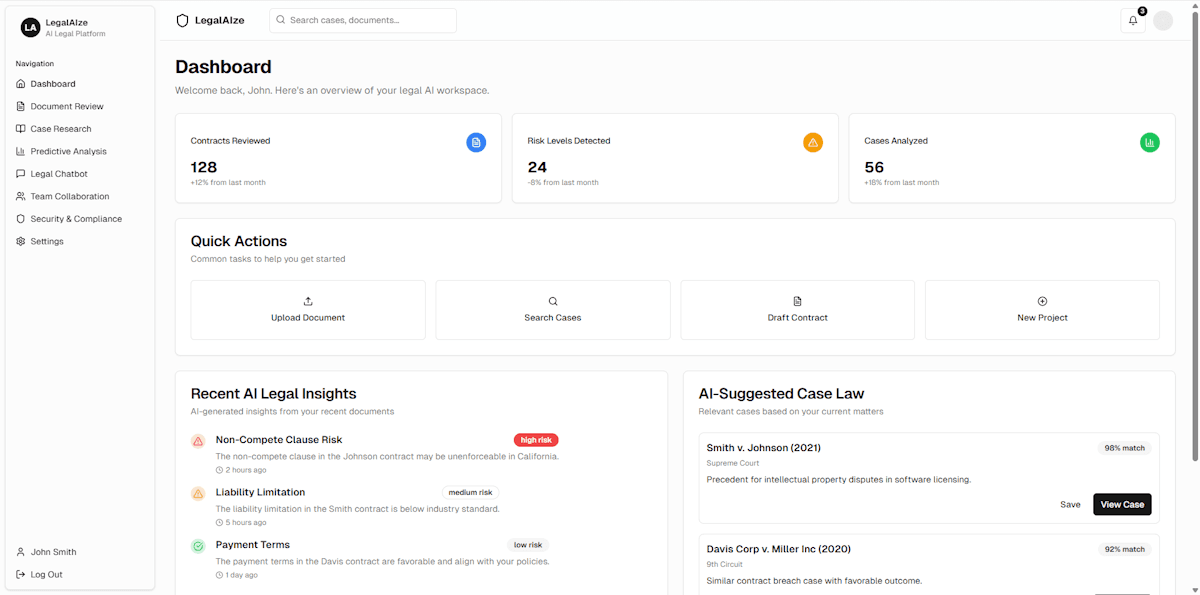
Legal Practice AI Automation
Automate contract analysis, discover case precedents, and get AI-powered legal insights in seconds, not hours.
Next.js / TypeScript / Prisma
Technologies we use
Industries it fits
Frequently asked questions
Do you do certified penetration tests?
We do security audits of code and applications. If you need a certified pentest report for a client or regulator, we'll connect you with a specialist firm and fix what they find.
How often should an app be audited?
At least once a year and after any major change. Dependency security updates should be applied monthly.
Do you help with GDPR?
Yes, on the technical side: encryption, data access, deletion on request and access logs.
Related services
Application Security in IașiWeb Application Development
We build complete web applications, from interface to database: customer portals, SaaS platforms, internal dashboards and tools that replace spreadsheets. We work with Next.js, TypeScript and PostgreSQL, and you own all the source code at the end.
Process Automation
We find the repetitive work in your company (copying data between places, generating documents, sending reports, chasing deadlines) and turn it into automated processes that run on their own and only alert you when a person is needed.
API Integrations
We connect the apps you already use (invoicing, accounting, online store, CRM, couriers, payments) so data flows between them automatically. And if you need others to connect to your system, we build the API.
Ready to Start Your Project?
Let's discuss how we can bring your vision to life with a custom web application that drives results for your business.